Third-Party Risk Management: Foundations for Practice
Understand how to identify, assess and oversee risks arising from suppliers and other external parties.
In person · Windhoek · 3–4 December 2026 · 12 CPE hours
Third-Party Risk Management: Foundations for Practice
In person · 3–4 December 2026
Course overview
Organisations rely on suppliers, service providers and other external parties to deliver important activities. This course explains why third-party risk management matters and how to build a workable programme from the ground up.
Participants explore the programme and relationship lifecycle, from governance and identifying third parties to due diligence, monitoring and exit. The course also examines implementation challenges, practical ways to address them and quick wins for getting started.
Who should attend
- Risk, compliance and governance professionals, and internal auditors
- Procurement, vendor-management, technology and information security professionals
- Legal, finance and operations teams involved in third-party relationships
- Students and graduates exploring careers in audit and GRC
What you will learn
- Explain what third-party risk management is, why it matters and how it complements procurement and contract management
- Identify third-party risks and assess the criticality of services and relationships
- Describe each stage of a programme and the responsibilities and outputs involved
- Apply proportionate due diligence, contracting and monitoring approaches
- Address implementation challenges with practical workarounds
- Identify quick wins and prioritise next steps for a programme
Learning approach
Practitioner-led discussion and scenarios help participants work through risk classification, due diligence and monitoring decisions. Exercises explore implementation barriers and help participants select quick wins and draft a proportionate programme action plan.
Included
Certificate of Completion
Issued after attendance of the full programme.
Full course materials
Slides, exercises and take-home notes.
TPRM framework and policy resources
Practical starting points for programme structure, roles, due diligence, monitoring and exit.
Facilitator
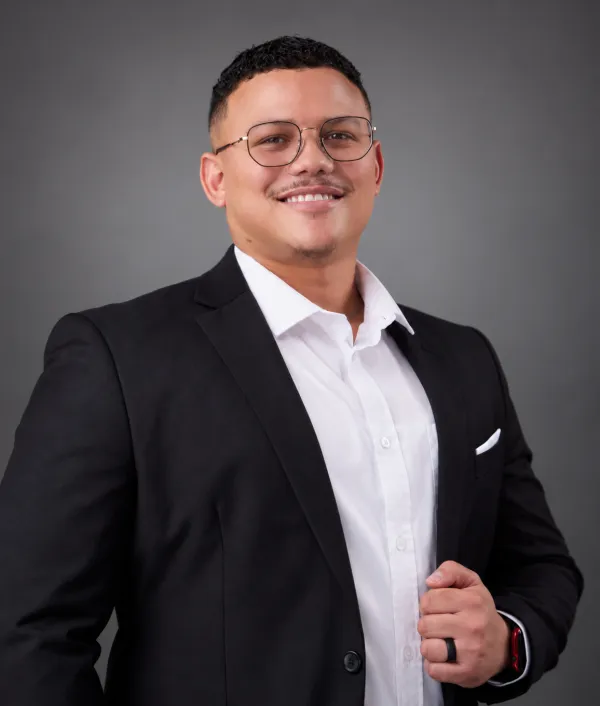
Morgan Beukes is an IT Risk and Information Security professional, currently serving as an IT Risk and Information Security Manager in the financial services sector. His experience spans banking and insurance, telecommunications, retail and logistics, with previous roles in ICT lecturing and IT Risk Advisory at a Big Four professional services firm.
Explore more courses
Browse every upcoming course or check dates on the training calendar.